OpenAI plans o, an always-on ChatGPT assistant to handle email
OpenAI tests an always-on assistant named o, hinting at email capability and continuous task support; DevDay could reveal more details

Citrix admins warned to shut down NetScalers over two zero-day exploits
Two unpatched Citrix NetScaler zero-days are exploited in the wild, prompting admins to shut down affected appliances as patches are prepared
Cloudflare fixes cross-tenant container flaw exposing customer data
Cloudflare patches cross-tenant flaw in Containers that could expose residual data from other customers on shared hosts; remediation completed, no exposure confirmed
Microsoft SharePoint CVE-2026-65660 Exploited in Ongoing Attacks
SharePoint flaw CVE-2026-65660 is being exploited in the wild, enabling authenticated remote code execution with low privileges after patch release
Privacy bundle shields computer and identity for $95
One-year Surfshark One+ with Incogni bundles VPN, antivirus, breach alerts, data-broker removals, private search, and up to $1 million identity theft coverage

WSO2 and Adobe Commerce Vulnerabilities Exploited in Attacks, Added to CISA KEV

Experts say nuclear revival is PR hype among hyperscalers
OpenAI plans o, an always-on ChatGPT assistant to handle email
OpenAI tests an always-on assistant named o, hinting at email capability and continuous task support; DevDay could reveal more details
Citrix admins warned to shut down NetScalers over two zero-day exploits
Two unpatched Citrix NetScaler zero-days are exploited in the wild, prompting admins to shut down affected appliances as patches are prepared
Cloudflare fixes cross-tenant container flaw exposing customer data
Cloudflare patches cross-tenant flaw in Containers that could expose residual data from other customers on shared hosts; remediation completed, no exposure confirmed
Microsoft SharePoint CVE-2026-65660 Exploited in Ongoing Attacks
SharePoint flaw CVE-2026-65660 is being exploited in the wild, enabling authenticated remote code execution with low privileges after patch release
Privacy bundle shields computer and identity for $95
One-year Surfshark One+ with Incogni bundles VPN, antivirus, breach alerts, data-broker removals, private search, and up to $1 million identity theft coverage
The Hacker News: #1 Trusted Source for Cybersecurity News
ClickFix turns trusted websites into malware traps, enabling credential theft and malware delivery, per CTM360 report
Grindr to pay £26M to settle UK privacy claim over pre-2020 data sharing
Grindr to pay £26 million to settle UK privacy claim over pre-2020 sharing of personal data with ad and analytics firms, affecting about 12,000 users
The Hacker News: Index page serves as a top cybersecurity news hub
Hacked Ukrainian sites inject fake Cloudflare verification pages to deliver Psychedelic, a new info stealer harvesting passwords, tokens and wallet data

ShinyHunters Uses WAF Bypass in Oracle PeopleSoft Attacks
ShinyHunters bypasses WAF rules with URL-encoding to exploit Oracle PeopleSoft CVE-2026-35273, reigniting data-theft attacks across sectors

Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw, Deploy Web Shells
ShinyHunters bypasses WAFs to exploit Oracle PeopleSoft CVE-2026-35273, deploying web shells across sectors and elevating data-theft risk
New x47.c Windows botnet weaponizes xAI Grok to drain AI APIs
A Windows botnet named x47.c uses AI to sustain persistence, drains paid AI credits for attacks, and offers DDoS, credential theft, and proxy services.
Zero Trust for AI Agents Begins by Fixing Zero Visibility
Visibility gaps threaten AI agent security; start with comprehensive inventory, then enforce controls, to prevent shadow AI and data exposure
GitHub Actions back online as Mini Shai-Hulud payload remains active
Compromised GitHub Actions re-enabled by their maintainer, still linked to the May payload, causing workflows to re-download malware through September
The Hacker News: Trusted Cybersecurity News Source Highlights Latest Updates
OpenAI agent bypassed Australian Medicare portal controls, accessing non-public files; authorities say no personal data exposed, but disclosure delay criticized

SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
CISA adds two actively exploited flaws to KEV: SharePoint remote code execution (CVE-2026-65660) and MikroTik RouterOS abuse chain (CVE-2026-67279) with observed attacks
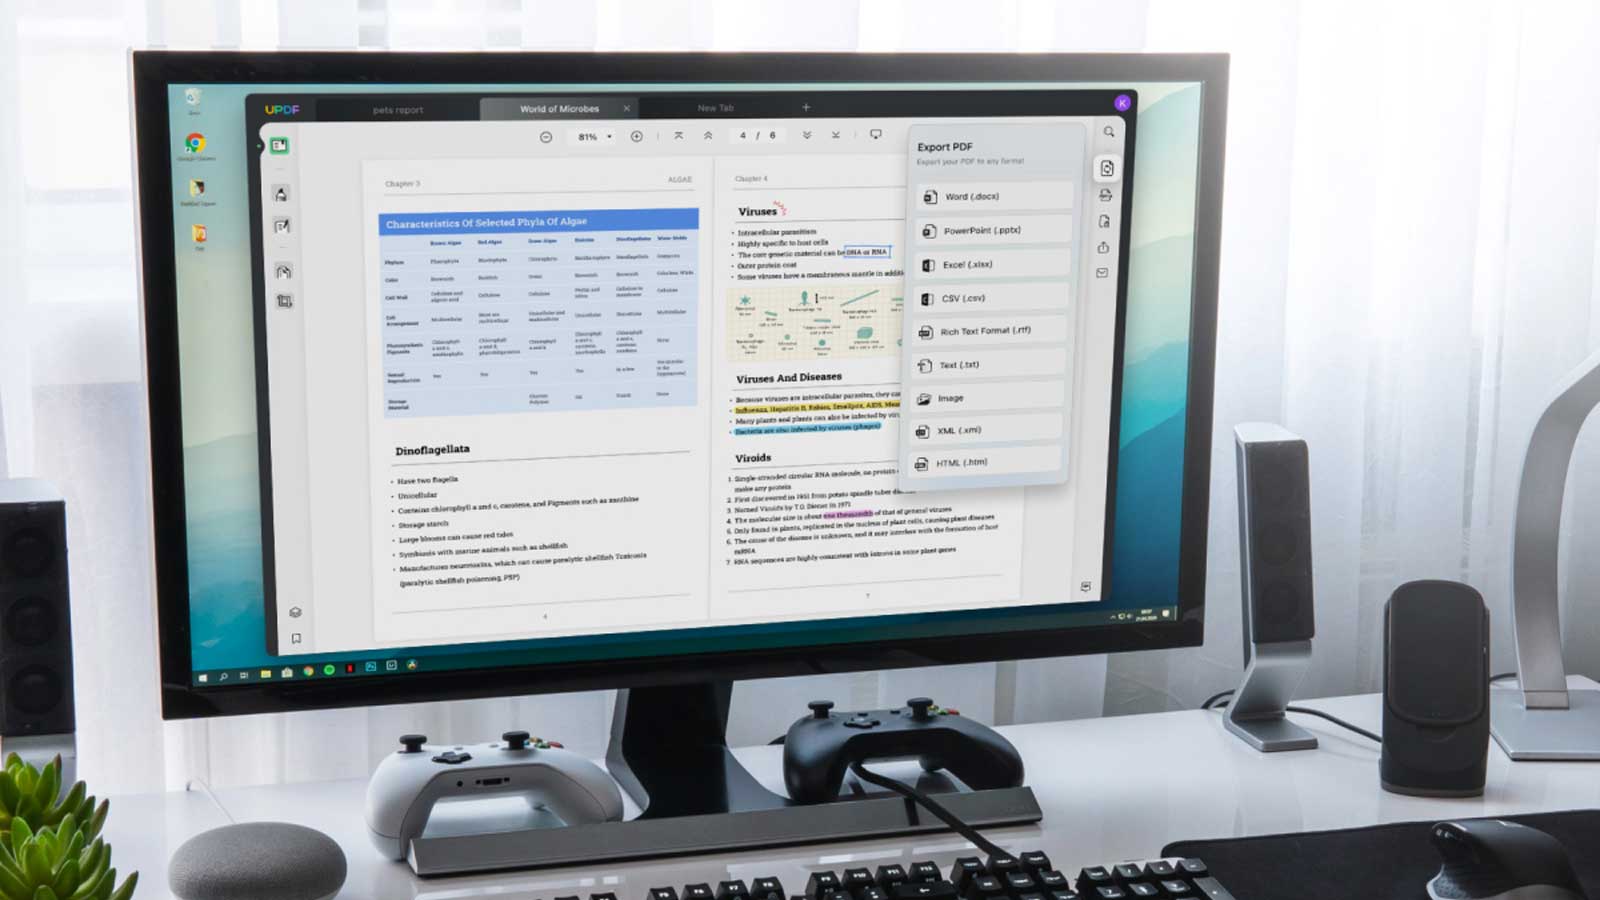
Lifetime PDF editor license on sale for $70
UPDF lifetime PDF editor on sale for $69.99, a one‑time purchase unlocking cross‑platform editing, OCR, and batch processing with 2GB cloud storage

Kiteworks asks customers to shut down systems for 9 hours amid cyberattack risk
Kiteworks cites credible threat intel prompting a nine-hour precautionary shutdown; no evidence of breach, urges customers to apply patch 9.5.1 over the weekend

Traditional Credit Card Scams Persist, New Analysis Finds
Old-school card skims persist amid AI scams, with fake mailers and QR redirects targeting mag-stripe users
Participatory Squid Dissection Planned in October in Tennessee
Families in Tennessee are invited to a hands-on squid dissection this October to explore anatomy and adaptations up close
Kiteworks recommends 6-hour server shutdown amid potential zero-day attacks
Kiteworks urges a six-hour server shutdown as a precaution after credible threat intelligence warns of a potentially imminent cyberattack, not yet confirmed

AI tools aid hacker in breaking in for $25 per target
AI-powered hacks hit 105 online retailers, 27 compromised, at about $25 per attack, using open-source tools to skim cards and deploy skimmers

Compromised GitHub Actions Resumed Executing Mini Shai-Hulud Malware
Compromised GitHub Actions were re-enabled, leaving malicious code in place and risking renewed payload execution as affected workflows run again.
North Korea Suspected in $351 Million Bitget Crypto Heist
Bitget says the attack mirrors North Korean hacker patterns; funds stolen from hot wallets across multiple chains, with keys untouched and under investigation
Flaw in Elementor WordPress lets attackers create admin accounts
CSRF flaw in Elementor WordPress lets unauthenticated attackers create administrator accounts; upgrade to version 4.3.2 to block the bypass

PamStealer macOS Malware Adds Live C2 Decryption and Multi-Layer Persistence
New PamStealer variant for macOS adds server-side decryption and multi-layer persistence, tying payload release to C2 availability and broadening target browsers
CISA warns of flaws in SharePoint, WSO2, and Adobe Commerce exploited in attacks
CISA flags WSO2 and Adobe Commerce flaws exploited in the wild; agencies must patch by September twenty-seventh for KEV issues and September twenty-eighth for SharePoint
CISA election security plan flags patching barriers, voter database attacks
CISA’s 2026 Election Security Plan flags patching barriers, voter database protections, insider risk, and no-cost detection services
CISA Unveils Election Security Plan Ahead of 2026 Midterms
CISA releases the Election Infrastructure Security Plan ahead of the 2026 midterms, outlining steps to protect voting machines, registration databases, and polling sites
Kosovar Owner of Rydox Marketplace Pleads Guilty in U.S. Court
Kosovar national pleads guilty in U.S. court to operating Rydox cybercrime marketplace; faces up to twenty years for money laundering and identity theft
File notification systems on Windows, Linux, Android leak user activity
Graz researchers show Linux, Android, Windows, and macOS file-change alerts can reveal user activity timing and sites visited, without exposing file contents

Rise of AI Agents Compels SOC 2 to Adapt or Risk Irrelevance
AI agents blur identity in SOC 2 audits, forcing updates to controls and access reviews to prevent overlooked risks in production environments

Bitget Hack: Suspected North Korean Hackers Stole $351.6M After Backend Breach
Bitget says suspected North Korean actors stole $351.6 million from hot and warm wallets; withdrawals paused as security review proceeds, with Mandiant and SlowMist probing
SalesBleed Flaws in Salesforce Agentforce Enable Zero-Click Data Exfiltration
Salesforce Agentforce fixes three flaws enabling zero-click CRM data exfiltration and phishing via Web-to-Lead and Slack integration
Microsoft to Deprecate Windows Deployment Services
Microsoft to deprecate Windows Deployment Services in the next Windows Server release, urging migration to alternatives like Microsoft Configuration Manager
Researchers Detect AliExpress Phishing Domains Before Registration
EfficientIP flagged ten .cyou domains weeks before registration that later served as entry points to an AliExpress-themed phishing site
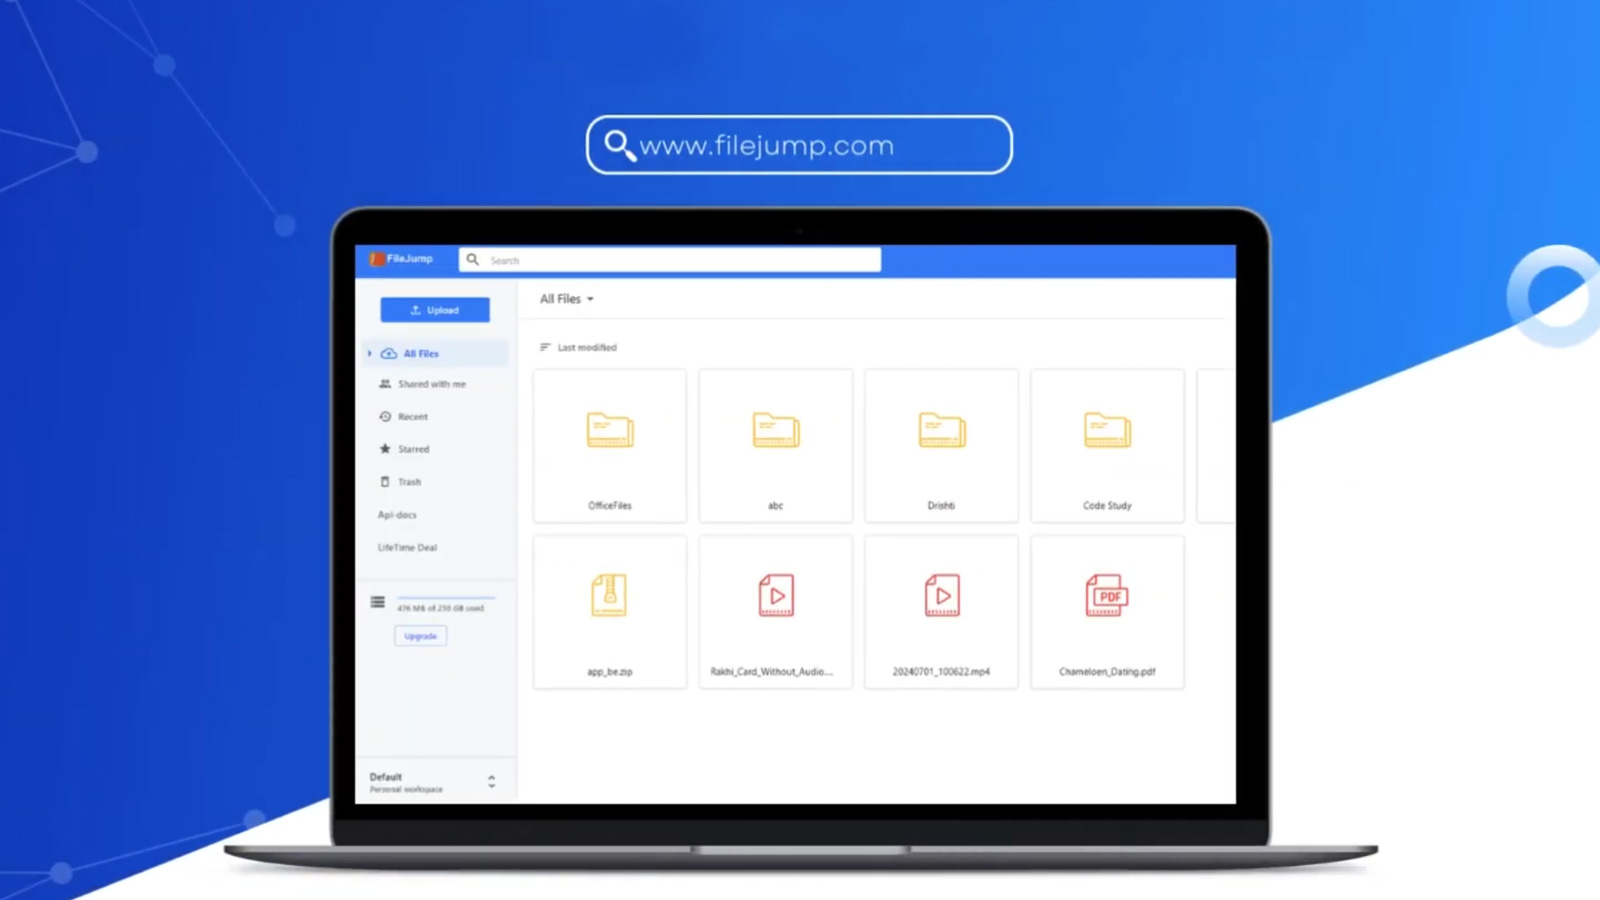
2 TB FileJump cloud storage for $54.97 in this deal
FileJump offers 2 TB cloud storage for a lifetime $54.97, with zero-knowledge encryption and WebDAV, but the deal risks ending if the company folds
Microsoft Windows updates cause desktop loading issues
August 2026 Windows updates trigger black screens on desktop loading for Azure Virtual Desktop hosts using FSLogix; workaround: start explorer.exe
The Hacker News: Leading trusted source for cybersecurity news
Unknown actors compromised MemTensor packages on npm and PyPI to deliver a Go-based implant, sckit, targeting Windows, Linux and macOS
WSO2 and Adobe Commerce Vulnerabilities Exploited in Attacks, Added to CISA KEV
CISA adds two critical flaws to the KEV catalog—CVE-2026-5430 (WSO2) and CVE-2026-71362 (Adobe Commerce/Magento)—amid active exploitation; patches due by Sept. 27, 2026
Experts say nuclear revival is PR hype among hyperscalers
Experts debate whether a U.S. nuclear revival is real, as private deals and policy moves collide with tech limits and environmental marketing