Success Case · Confidential Client
Identity Resilience
From access governance to continuous detection of identity threats.
“When signals are scattered across different systems, each tool provides only part of the context.”
How QRIAR took the identity program for a large multi-brand restaurant chain—with more than 300 locations—comprising IGA and PAM, and expanded it to include behavioral detection using IBM Verify Identity Protection.
Why weren't IGA and PAM enough for a chain of more than 300 restaurants?
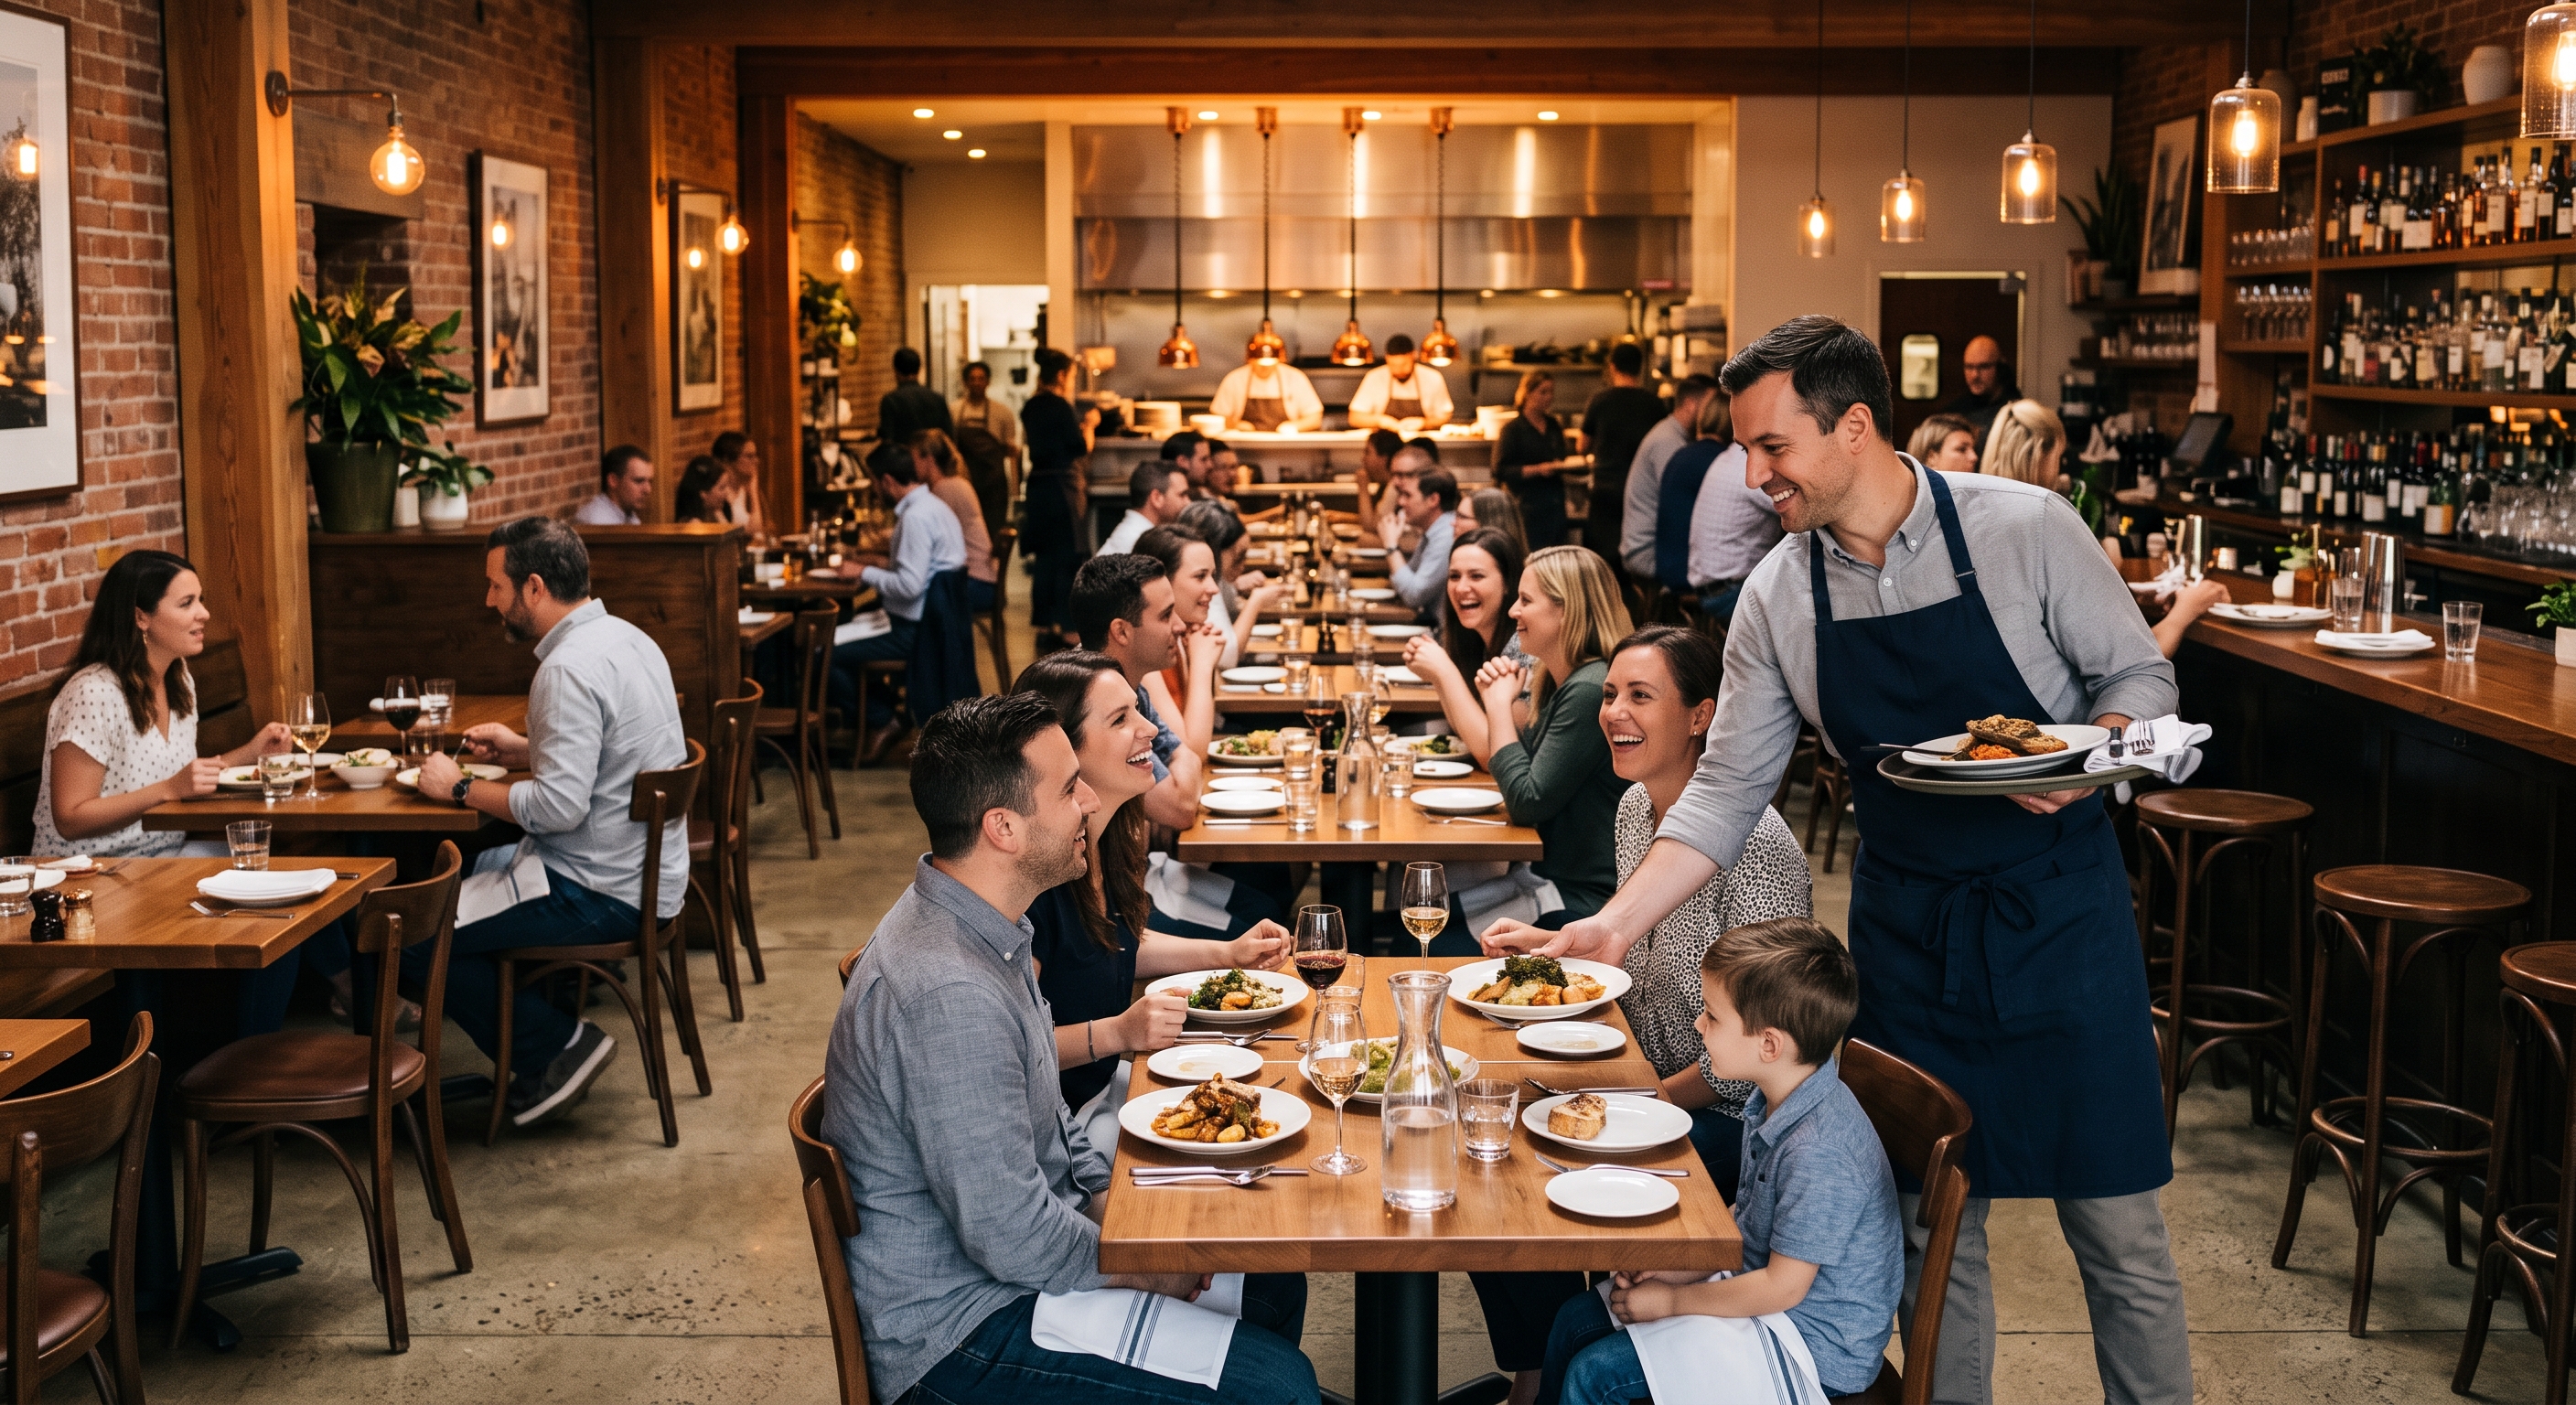
The client is a large Brazilian restaurant chain with more than 300 locations spread across dozens of cities, two proprietary brands, and a recently launched international expansion. Thousands of employees support the operation, with in-house production and logistics that integrate supply and distribution. In this context, digital identity ensures that employees and third parties can access the necessary resources in a secure and controlled manner. The identity and access management journey began a few years ago with IBM IGA and PAM solutions in an on-premises environment, establishing access governance and the protection of privileged credentials. As the program matured, new licenses were activated, more areas and systems were brought under governance, and additional teams were onboarded into PAM. This expansion created a new need: to identify identity risks more broadly and respond more quickly. As the ecosystem grew, so did the volume of signals generated by directories, applications, privileged access, and security controls. IGA and PAM remained essential, but they needed to be supplemented with a continuous behavioral view of identities, exposures, and anomalies.
How can you speed up response times with a lean team?
Identifying the risk is only the first step. With a small team, investigations and manual responses
take up time that could be devoted to the most critical cases—and, without
correlation, linking users or non-human accounts to observed activities delays the identification of anomalous patterns. To move forward in this phase, the client implemented IBM Security Verify Identity Protection, adding a layer of ITDR—Identity Threat Detection and Response—to the IAM program. The solution correlates signals and behaviors to identify risks and exposures associated with identities.
How did IGA, PAM, and ITDR come to operate as a single program?
The client relies on QRIAR, a company specializing in cybersecurity and identity and access management, to support this evolution. QRIAR has been working with the client since the initial implementation of IAM and is involved in architecture planning, the implementation and integration of IBM VIP, the definition of use cases, and tailoring the solution to the environment. The design complements existing controls rather than replacing them: IGA governs who should have access to corporate resources; PAM protects credentials, accounts, and sessions associated with critical privileges; and IBM VIP monitors identity usage, prioritizes risks, and flags situations requiring investigation or intervention. The solution also includes customized responses that link identified risks to mitigation actions in other systems, such as credential sources and access control platforms. It is this connection between detection and action that
shortens the path from alert to mitigation—while preserving human analysis where context
requires a decision.
What results was the ITDR layer designed to deliver?
Expanded visibility — risks, anomalies, and identity behaviors viewed within a broader context, rather than as isolated signals from individual tools.
Contextual prioritization — events and investigations sorted by context and business criticality.
Less manual effort — reduced repetitive work in analyzing and handling recurring situations.
Faster response — shorter time between identifying a risk and implementing mitigation measures.
Better utilization of a lean team — operational capacity focused on cases requiring specialized analysis.
Traceability and auditing—history of identities, accesses, and actions, with simplified auditing processes.
What's next: from visibility to response?
One of the initiative’s central goals is to translate the visibility gained through ITDR into practical actions. Based on the identification and prioritization of risks, the program can evolve to include customized and conditional workflows—such as opening an investigation, notifying teams, blocking, or
suspending access—defined according to context and criticality.
For the business, this evolution translates into greater protection of access to critical systems such as POS, inventory, and financial systems; reduced exposure to internal fraud; and an identity foundation
ready to support growth
“The goal is to reduce the time between detection and action, without replacing human analysis.”
Execution.
From a team you can trust.
Talk to QRIAR about identity threat detection and response in your operation.